The Twenty-Eight Questions Behind Your Next Fraud Investigation
CMS has a draft contract out for the entity that investigates providers, and it moves lead generation and final sign-off to CMS itself. Responses close November 4, and the manual that governs the current model is the one CMS told respondents to ignore.
If you have ever opened a records request from a program integrity contractor, you have met the entity that picked your name out of a claims file. Under the manual that governs it today, that contractor picked your name on its own authority.
CMS is asking the market whether that should stop.
Solicitation 270536, "Fraud Defense Contracts," went onto SAM.gov on October 5 and was revised on October 13. It surfaced in MLN Connects this morning with one paragraph and a deadline: responses close at 11:00 a.m. ET on November 4, six days out.
CMS says in the same breath that it will not award a contract from this. True, and beside the point.
Two PDFs hang off the notice. One is a six-page draft Statement of Objectives for the contract that succeeds the program integrity model you work under now.
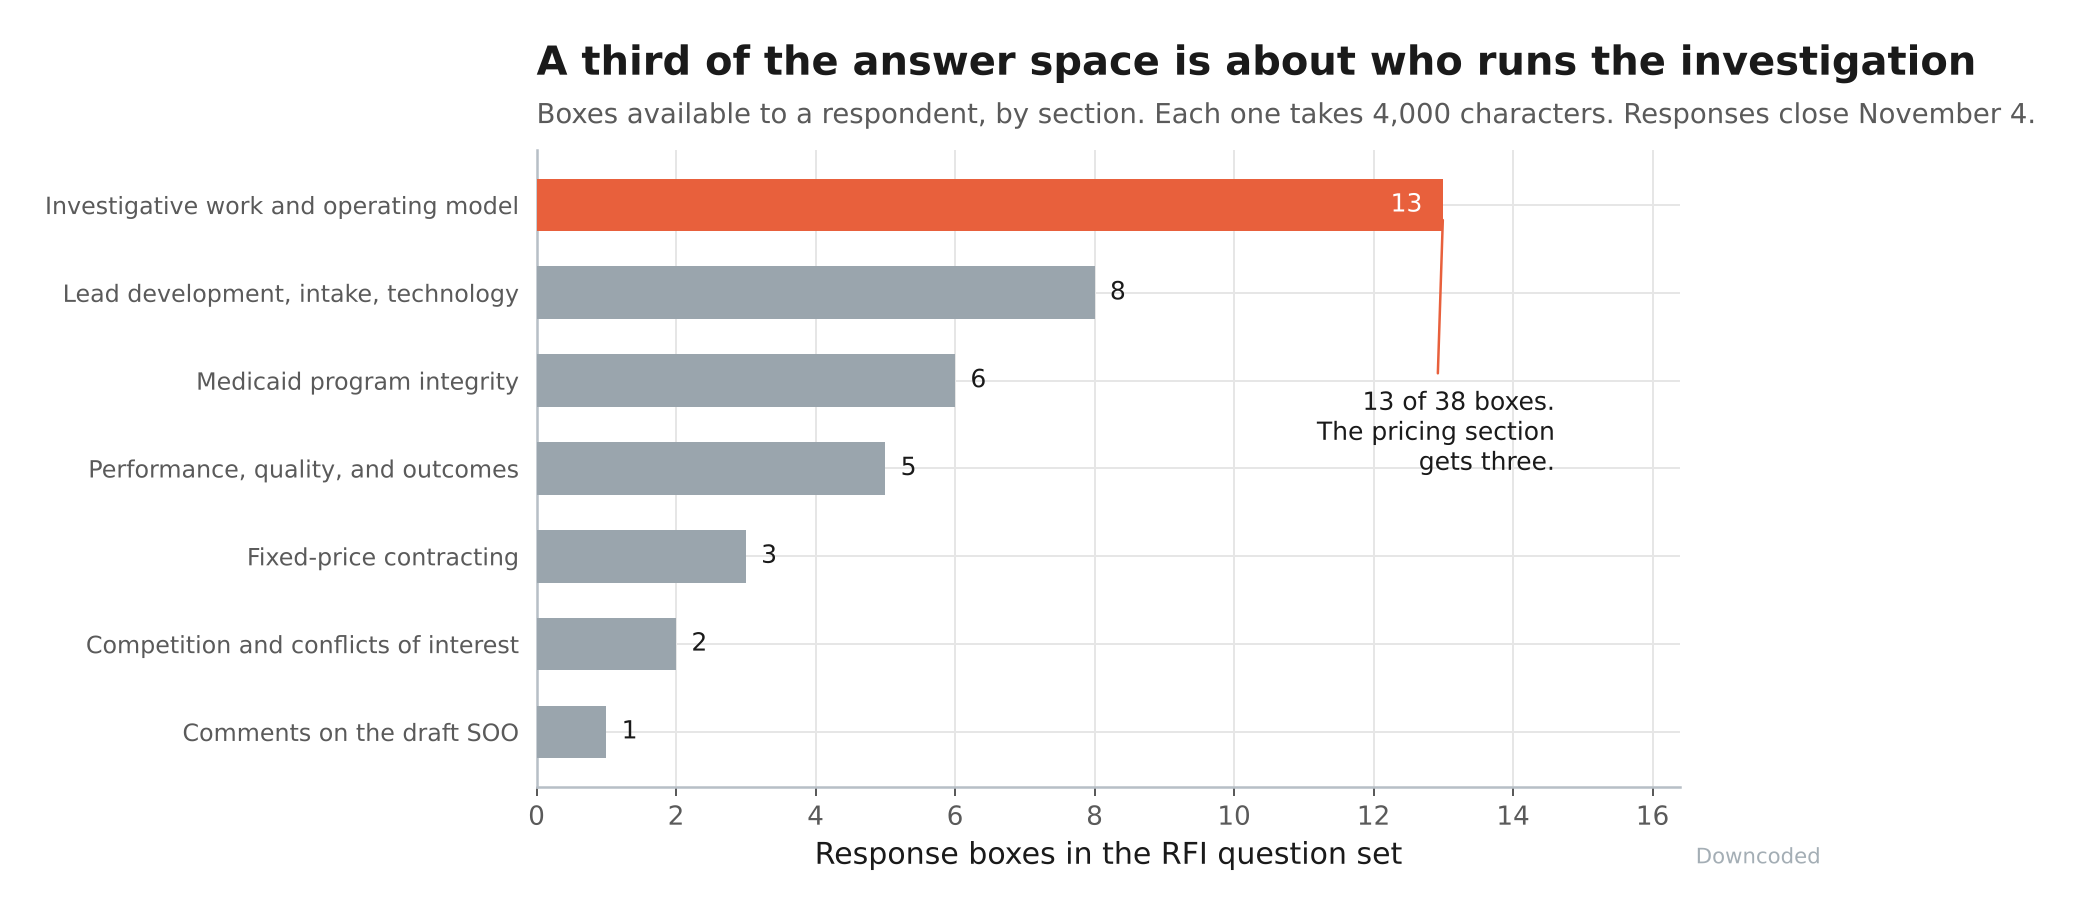
The other is a 41-page question set with 38 response boxes at 4,000 characters apiece. That is 152,000 characters of industry opinion CMS is soliciting on how it should investigate providers.
Thirteen of those boxes sit in a single section (chart below).
"Who gets to decide your claims are worth a second look?"
The rest of this brief is for subscribers.
The impact tables, the code-level detail, and the rest of the analysis sit past this line.
$50 a month, or $500 a year.
Already a subscriber? Sign in